Personal AI Agent Permissions: What To Know Before You Connect
Meta’s Muse, OpenAI’s Dots, Grok Bot, Instinct, Fo, Tab, Hark. The list of personal AI agents keeps growing, and the pitch is the same across all of them: give the agent a task, and let it run.
Running is where it gets serious. Depending on the agent and the task, running can mean reading your email, opening sensitive documents, contacting customers, or spending money. You are giving software permission to act in your name, in places where mistakes carry a real cost.
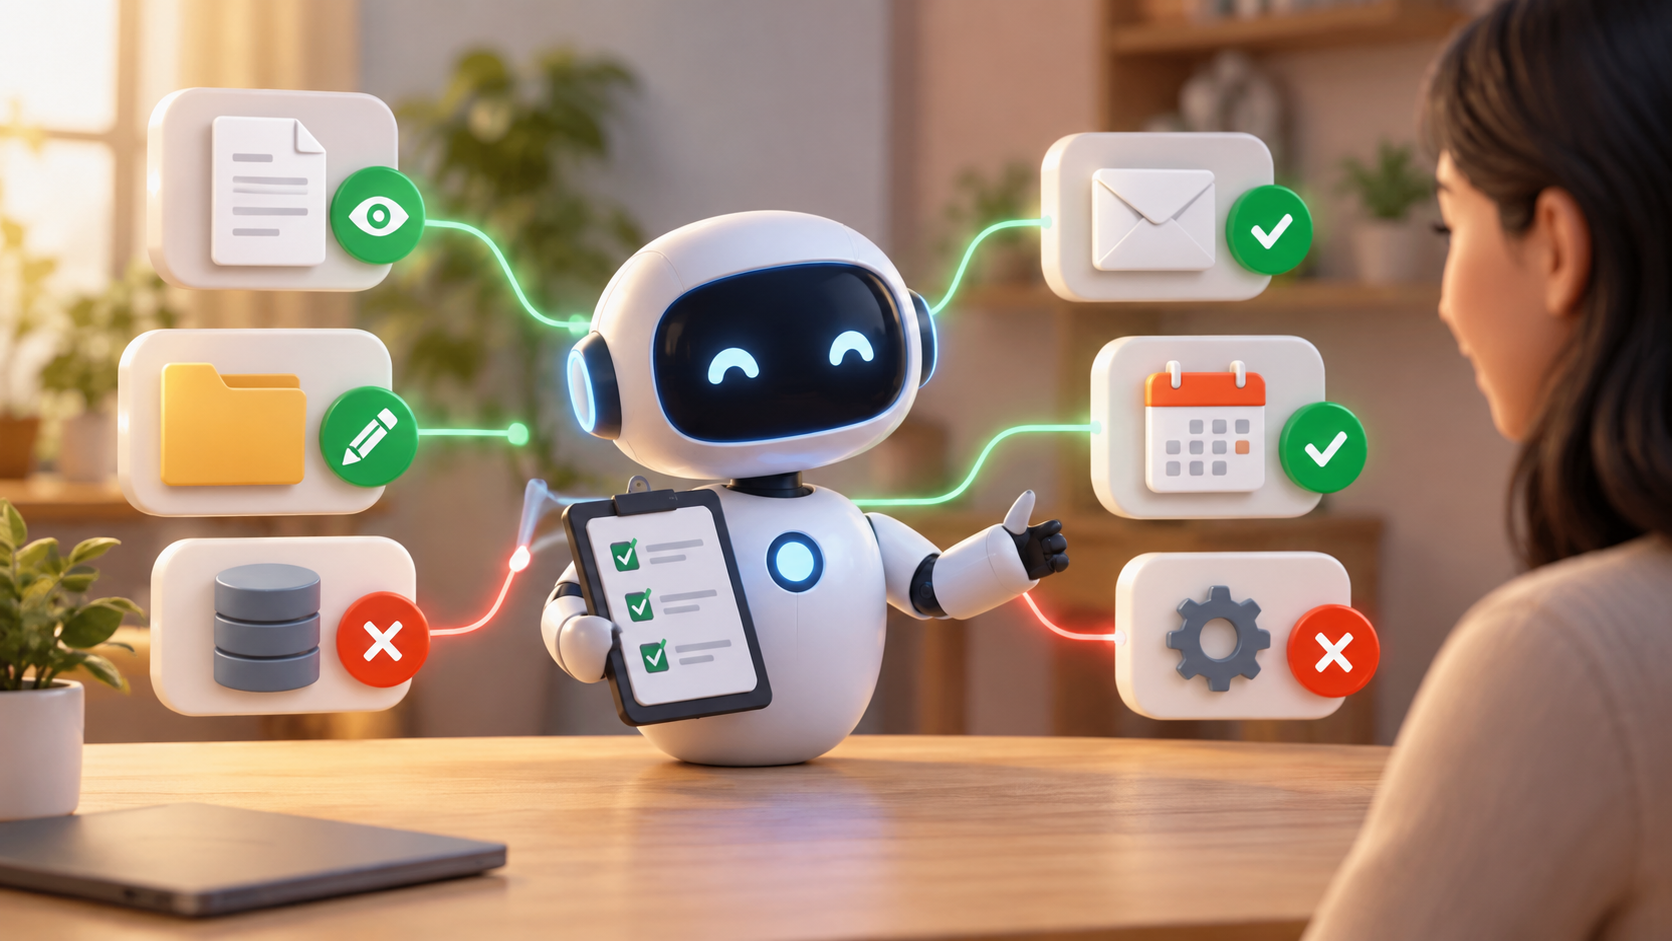
Personal AI agent permissions are the rules that decide what an agent can read, what it can change, and which actions it can take in your name without asking you first. They deserve as much scrutiny as the task you hand the agent.
Most people set them in about three seconds, on a screen that ends with an “Allow” button.
What “Help Me Manage My Inbox” Actually Authorizes
Take a request most owners would happily hand off: “Help me manage my inbox.”
Does that mean summarizing messages? Drafting replies? Sending them? Deleting emails? One sentence, four very different permissions.
| What the agent does | If it gets it wrong | |
|---|---|---|
| Summarize | Reads your messages and reports what matters | You miss something important, or act on a summary that got it wrong |
| Draft | Writes replies that wait in your drafts folder | You fix the draft before it goes out. Nothing has left the building |
| Send | Writes replies and sends them as you | A customer gets a wrong price, a wrong tone, or a promise you never made |
| Delete | Removes or archives messages it judges unimportant | A contract, an invoice, or a complaint disappears before anyone reads it |
The first two rows keep you in the loop. The last two take you out of it. The risk changes completely between drafting and sending, and the request sounds identical either way.
The same split shows up everywhere an agent works. An agent can prepare a customer quote without being allowed to send it. It can compare suppliers without placing an order. It can check your availability without reading every calendar detail. Preparing the work and acting on it are separate permissions, and a lot of the time an agent saves you sits in the preparing.
The Three Boundaries to Set Before You Connect
Before connecting an agent to your email, files, or business accounts, write down three things. Writing them matters: a boundary you can state in one sentence is a boundary you can check later.
1What It Can Read
Reading feels harmless because nothing changes. It still matters. An agent with read access to your inbox sees client details, pricing, contracts, and anything someone forwarded to you by mistake.
It can also be steered by what it reads. An incoming email can contain instructions written for the agent instead of for you, and an agent that treats everything it reads as a request is easy to misdirect. Security researchers call this prompt injection, and it is one more reason to keep reading access narrow.
Narrow it to the task. A scheduling agent needs your free and busy times, not the subject line of every meeting. An agent drafting quotes needs your price sheet, not the whole shared drive.
2What It Can Change
Changing covers anything that leaves a mark: creating drafts, editing documents, moving files, updating a customer record, adding calendar events. Some changes are easy to undo. A draft can be deleted. An overwritten spreadsheet or an edited CRM record may not come back cleanly.
Decide which systems the agent can write to, and keep the first list short.
3Which Actions Need Your Approval
Some actions should always stop and wait for you. A reasonable starting list for most small businesses and nonprofits:
- Anything a customer or partner will see. Sent emails, messages, quotes, and posts.
- Anything that spends money. Orders, bookings, subscriptions, and payments.
- Anything hard to reverse. Deleting messages or files, cancelling appointments, changing account settings.
- Anything that shares information outside the business. Forwarding documents, filling in forms with company details, granting access to someone else.
Approval only protects you if you read what you approve. Meta acknowledged this when it launched Muse in September 2026, saying it wanted to keep users from approving requests on reflex. An approval screen you click through twenty times a day stops being a safeguard by the end of the first week.
Check That the Tool Enforces Those Boundaries
Defining the boundaries is half the job. The other half is confirming that the agent’s settings can hold them.
The newest agents ship with real controls. Muse routes its actions through a separate access system that can allow an action, block it, or send it to you for approval, and it lets users separate read access from write access, scoped to a task, a service, a transaction, or a time period. OpenAI’s Dots, launched at the end of September 2026, keeps app connections read-only while the agent researches on its own initiative, and puts actions that touch your accounts through an automated review first.
Those controls exist. Whether they are switched on for your account, set the way you assume, and applied to every app you connect is something you confirm yourself. Before connecting, look for:
- A read and write split for each service. You should be able to let the agent see your calendar without letting it edit your calendar.
- Approval that blocks. The action waits until you say yes, instead of going ahead and notifying you afterward.
- An activity log. A record of what the agent read, drafted, sent, and changed, in a form you can review in five minutes.
- A clear data-use setting. Whether your messages and files can be used to improve the provider’s models, and where to turn that off. Meta, for example, uses queries by default and lets users opt out.
- A fast way to disconnect. One place to revoke the agent’s access to each account, taking effect immediately.
If a setting you need isn’t there, the boundary only exists on paper. Narrow the task until the tool’s actual controls match it, or keep that task manual for now.
When Employees Bring Their Own Agents to Work
All of this becomes more urgent once employees bring their own agents to work. Someone may connect the assistant they use for dinner reservations to their company inbox without considering what access they’ve granted.
When that happens, the agent can inherit much of what the employee can reach. If that employee’s login opens the shared client folder, the CRM, and the accounts-payable inbox, the agent may reach them too. And the data-use settings that apply are the ones on the employee’s personal plan, which the business never reviewed.
Providers are starting to separate personal agents from work agents. Alongside Dots, OpenAI previewed specialist agents that an employer provisions with their own identity and credentials for one defined job, with procurement and invoice processing among the early tests. That separation puts the decisions where they belong: the business sets the job, the access, and the identity, instead of inheriting them from whatever an employee connected on a Sunday afternoon.
Teams need clear rules about which agents can connect to work accounts, and on what terms. Those rules usually cover four things:
- Which agents are approved. A short named list, reviewed when new tools arrive.
- Which accounts they can touch. Email and calendar may be fine. Finance and client records may need a higher bar.
- What always needs a human. The approval list above, applied to every agent, personal or company-provided.
- What happens when someone leaves. Agent access is revoked along with the employee’s other accounts.
Written rules are the start. The conversation matters as much. People connect personal agents to work accounts because the agent saves them time, and a rule that ignores that reason gets quietly worked around.
Where the rules live
A policy that says “don’t connect unapproved agents” covers the risk. It doesn’t show anyone how to use the approved ones well. An AI Manual does that, turning the rules into steps your team can follow on an ordinary Tuesday.
Start With One Narrow Task
Start with one narrow task and minimal permissions. Review what the agent does. Expand access only when you have a clear reason and safeguards in place.
For an inbox, that can look like this. For the first two weeks, the agent reads your inbox and sends you a morning summary. Nothing else. You compare the summary against what you received. If it holds up, the next step is drafting replies that stay in your drafts folder. Sending stays with you until the drafts consistently need no edits, and for anything going to a client, it may stay with you for good.
Each step adds one permission, and each permission is earned by what the previous step showed you. That pace feels slow next to the launch demos. It is also how you learn what the agent gets wrong while the cost of a mistake is a bad summary instead of a sent email. Scoping small like this is a large part of what AI fluency for teams looks like in practice.
The convenience is real. So is the authority you’re handing over.
Before you click “Allow,” be clear about what you’re allowing.
Frequently Asked Questions
What are personal AI agent permissions?
Personal AI agent permissions are the rules that decide what an agent can read, what it can change, and which actions it can take in your name without asking you first. They are set when you connect the agent to an account, and they keep applying long after you’ve forgotten the setup screen.
Is read-only access safe to give an AI agent?
It is lower risk than write access, but not risk-free. An agent that reads your inbox or files sees client data, pricing, and contracts, and that data falls under the provider’s data-use settings. The agent can also be misdirected by instructions hidden in content it reads, so read access should still be limited to what the task needs.
Do approval prompts make an AI agent safe?
Approval prompts help only when they stop the action until you respond, and only when you read them before clicking. If an agent asks for approval constantly, people start approving on reflex. Keep approvals for actions that face customers, spend money, share information, or are hard to undo.
Can employees connect personal AI agents to work accounts?
Often they can, through their own login, and the agent may then reach much of what that employee can reach. Whether they should is a business decision. Without written rules on approved agents, allowed accounts, and required approvals, each employee makes that decision alone.
What should a small business do first?
Pick one narrow task, connect the agent with the minimum access that task needs, and review its activity for a couple of weeks. Write down what it can read, what it can change, and which actions need your approval, then confirm the tool’s settings enforce each one.
Digismart
Find out which AI tools already touch your accounts
Digismart helps small businesses and nonprofits set up AI tools with clear access, approval rules, and training for the people who use them. An AI audit maps which tools connect to your systems and what they can reach, in plain language.
Book an AI Audit Prefer to start with your team? See our AI workshops